Skip to content
Feature · Server-side tracking

Collection that does not depend on the browser

Events are captured on our infrastructure, from your own domain, and forwarded to ad platforms over API. The browser stops being the single point of failure between a sale and the report you optimize against.

98% Match rate, server-side
<5 min Setup, one snippet
~10KB Gzipped, loaded async
30 to 40% Of conversions a pixel alone misses
How it works

Four hops, none of them fragile

01
Own-domain collection A CNAME puts the endpoint on track.yourdomain.com. Requests are first-party and indistinguishable from your site.
02
Click ID persistence gclid, gbraid, wbraid, fbclid and msclkid are stored server-side, outside the seven-day cookie ceiling Safari enforces.
03
Enrichment and hashing Events are matched to the stored identity, PII is SHA-256 hashed, and a shared event ID is attached for dedupe.
04
API forwarding Delivered to Google Ads and OpenAI Ads over their conversion APIs today, with retries and per-event status. Meta, Microsoft Ads and TikTok are coming soon.
index.html~10KB gzipped, default install
<script async
  src="https://cdn.convultra.com/ultra.min.js"
  data-convultra-key="proj_…">
</script>
checkout.js
Convultra.trackPurchase({
  value: 149.00,
  currency: 'USD',
  orderId: 'ORD-12345',
});
In the product

What you see once it is running

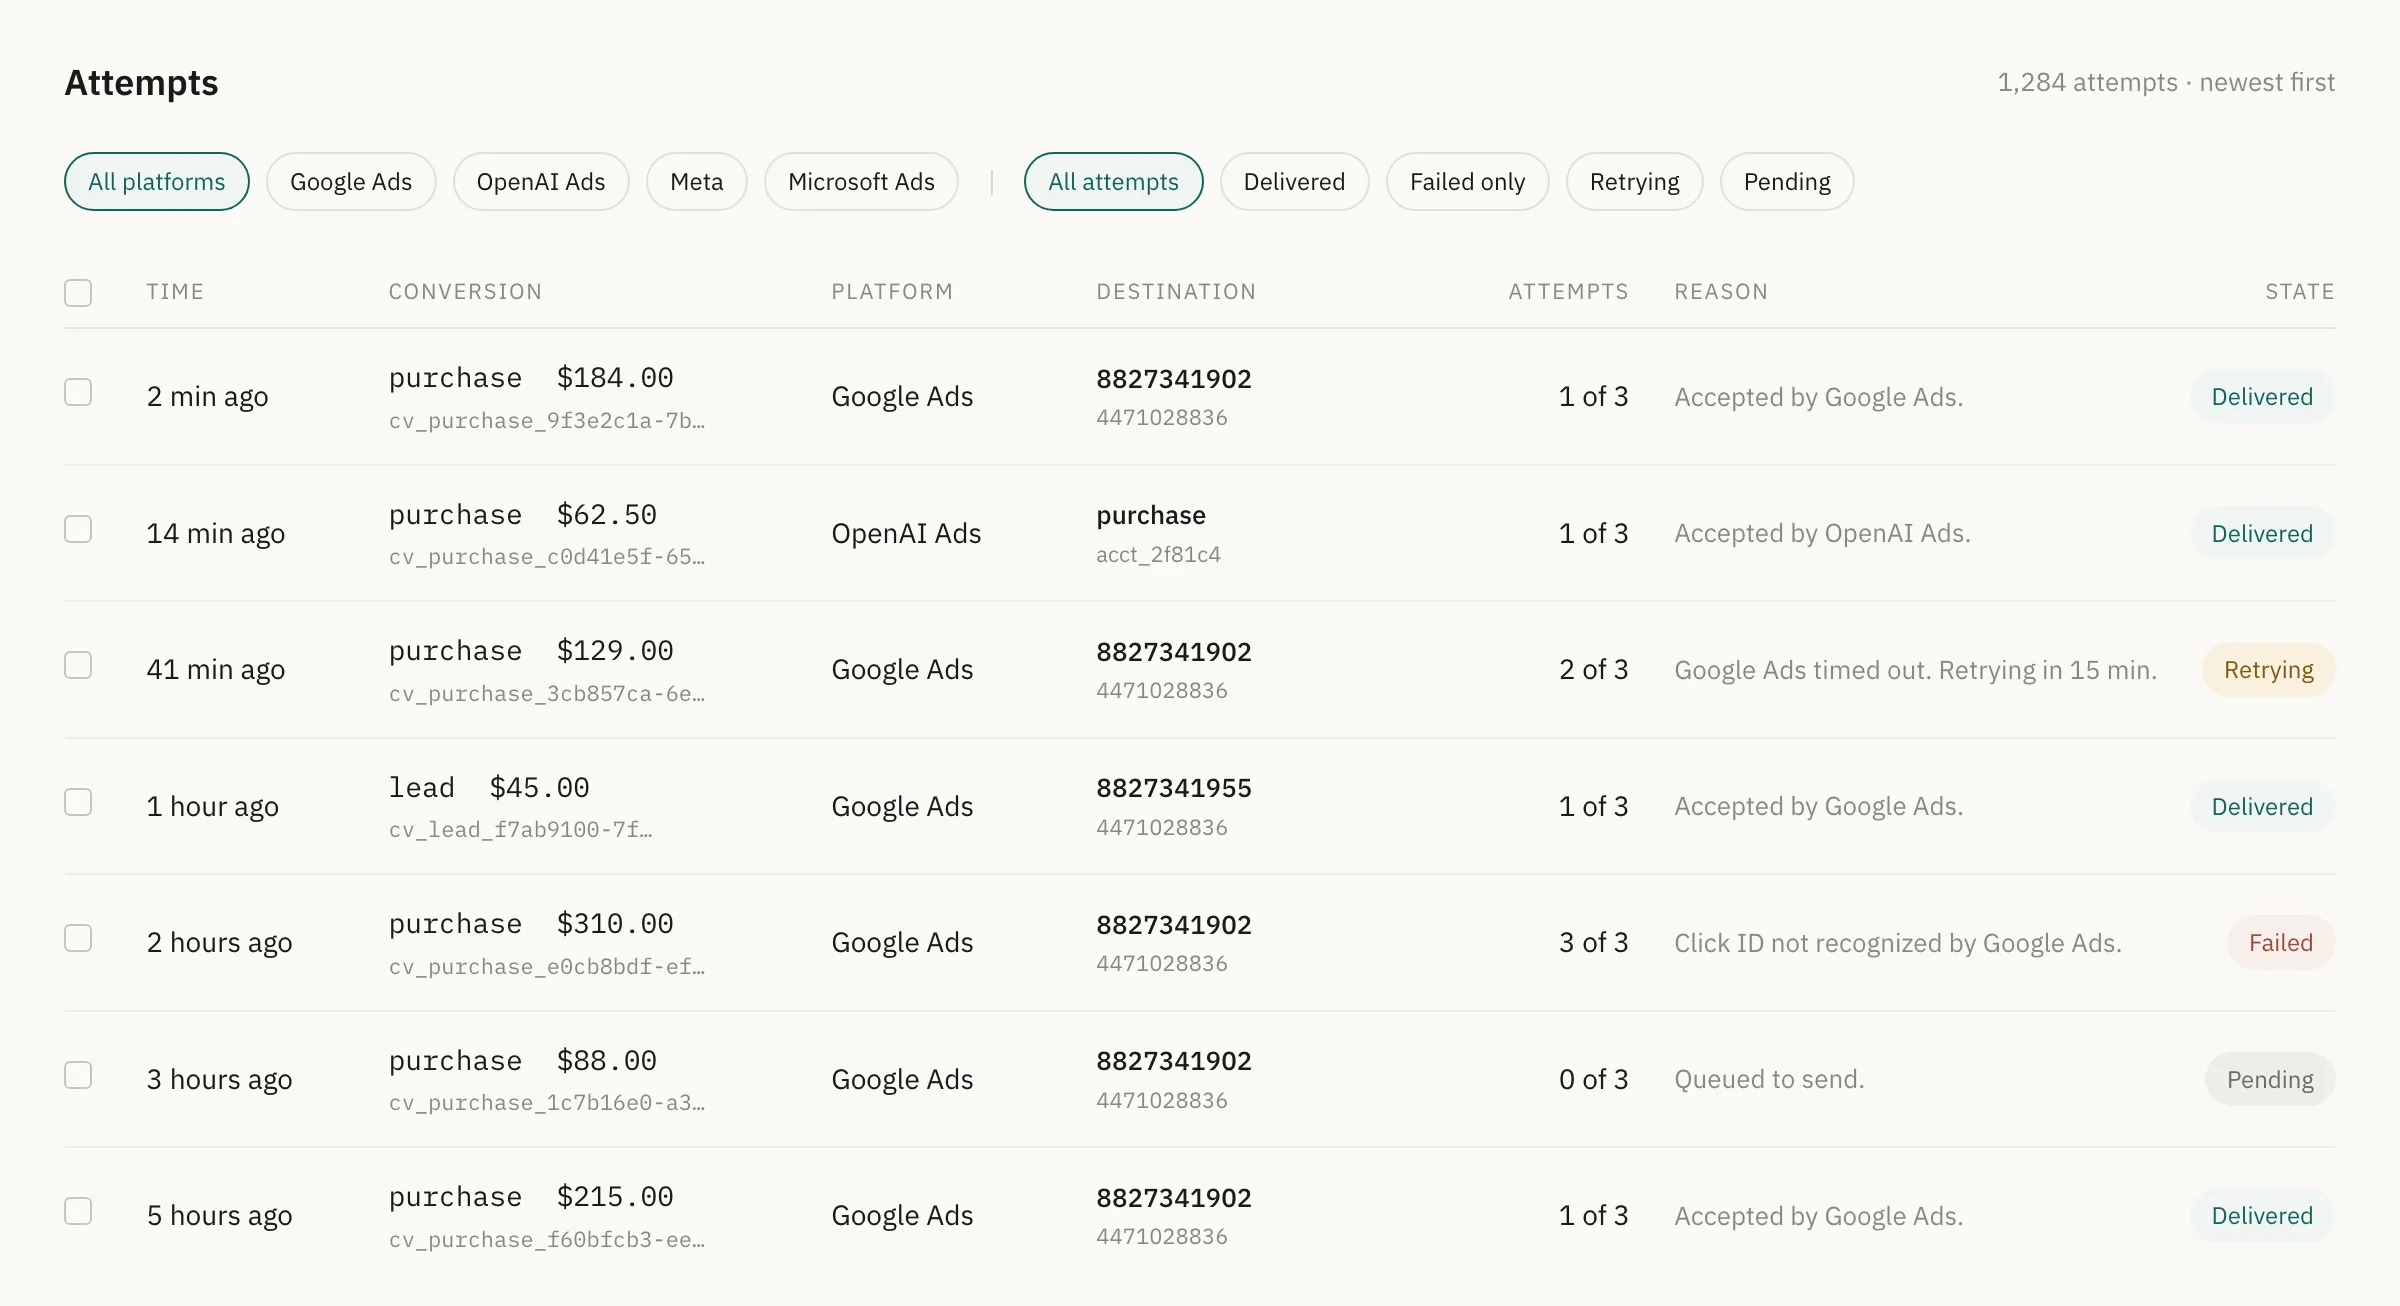
Conversion delivery attempts in Convultra: each purchase or lead with its value, the platform destination, attempt count, the platform response and its delivery state.
Every conversion, with proof it reached the platform
What it survives

The things that break pixels

Ad blockers A meaningful share of traffic blocks pixel endpoints outright. First-party collection is not on those lists.
Safari ITP Client-set cookies expire in seven days, or 24 hours on link decoration. Server-set identity is unaffected.
Firefox ETP Total Cookie Protection partitions third-party state across sites. Nothing in this flow is third-party.
Long windows B2B and high-ticket purchases attribute weeks after the click rather than landing in Direct traffic.
Missed thank-yous The order is captured from your backend, not from a confirmation page the customer may never load.
App-to-web hops In-app browser handoffs keep their click ID instead of starting a fresh anonymous session.
Specifics

For whoever asks the technical questions

Collection First-party CNAME subdomain
Script ~10KB gzipped, async, no render block
PII handling SHA-256 hashed before transmission
Click IDs gclid, gbraid, wbraid, fbclid, msclkid
Consent Respects consent: when a visitor declines tracking, nothing is recorded or forwarded
Retention 3 to 24 months of analytics by plan
Deduplication Shared event ID across browser and server
Reliability Automatic retry with per-event delivery log

Before you install

Do I need a developer to set up server-side tracking?

No. Paste the script in your site header or install the WordPress plugin, connect your ad accounts, and the server-to-server delivery is handled for you. Most accounts are live in about five minutes.

Do I still need my Google tag or Meta pixel?

Keep them. Convultra runs alongside them and deduplicates with shared event IDs, so nothing is counted twice and you can compare the two feeds during your trial.

Does this get around consent?

No. Convultra respects consent: when a visitor declines tracking, nothing is recorded or forwarded. Server-side tracking is about surviving technical blocking, not evading privacy choices.

Which platforms receive the conversions?

Google Ads and OpenAI Ads today, including enhanced conversions on Google Ads. Meta, Microsoft Ads and TikTok forwarding are coming soon.

Next

Pairs with

Paste one script. Count everything.